
Update Notices for Teamscale 2026.8
2026.7 Deprecated: RTC/Jazz Connectors, Crowd Authentication, Legacy Code Mapping, Xodus Storage Backend
Deprecated IBM RTC/Jazz Connectors
The IBM RTC/Jazz issue tracker connector and the IBM RTC/Jazz requirements management connector are deprecated and will be completely removed with version 2026.9.
Action required: If you still connect a project to RTC/Jazz, please contact us before upgrading to 2026.9.
Deprecated Crowd Authentication
The Crowd Server authentication option is deprecated and will be completely removed with version 2026.9.
Action required: If you authenticate your users via Crowd, switch to LDAP or single sign-on via SAML 2.0 or OpenID Connect before upgrading to 2026.9. If neither fits your setup, please contact us.
Deprecated Legacy Code Mapping in Architectures
The Enable legacy code mapping option in the architecture editor is deprecated and will be completely removed with version 2026.9. It was introduced as a fallback to the mapping behavior of Teamscale 7.7 and earlier, where the include and exclude patterns of a component were evaluated independently of those of its parent components. This option was set for architectures created before Teamscale 7.8 and is off by default for architectures created afterwards.
Once the option is gone, all architectures are assessed with the current behavior: a type or file is mapped to a subcomponent only if the mappings of its parent components match it as well, and an exclude pattern of a component also applies to its subcomponents.
Action required: Manual action may be required if an architecture with the legacy mapping option contains nested components and the parent component has non-empty include/exclude patterns defined. In this case it is recommended to switch off the legacy mapping setting prior to the 2026.9 update and reworking the code mappings as follows. Widen the include patterns of the parent components so that they also match what their subcomponents map, and remove exclude patterns that you do not want to apply to the subcomponents. Use the Unmatched Types panel of the architecture editor to find code that is no longer mapped, and check the assessment for components that lost their content. If you need help with the migration, please contact us.
Deprecated Xodus Storage Backend
The xodus value of the database.type option is deprecated and will be completely removed with version 2026.9.
Action required: If your teamscale.properties sets database.type=xodus, switch to the default rocksdb before upgrading to 2026.9.
2026.6 Security: TLS certificates for LDAP connections are now validated
Teamscale will now reject expired or untrusted certificates. Self-signed certificates must be added to the JVM Trust Store to connect to an LDAP server via HTTPS.
2026.6 Cppcheck Premium: MISRA C edition moved from 2023 to 2025
The Cppcheck Premium integration now uses the MISRA C:2025 edition instead of MISRA C:2023. Accordingly, the check IDs of all MISRA C rules change from premium-misra-c-2023-* to premium-misra-c-2025-*. Existing findings and their tolerations are carried over across the rename, and analysis profiles are migrated automatically on upgrade.
The three changes below, however, drop the enablement setting of individual rules, no matter whether you had explicitly enabled or disabled them. Tolerations are not affected.
Action required: If you have customized any of the rules or checks listed below, review and re-apply your settings after upgrading.
- Rules absorbed into other rules are removed: MISRA C:2025 merged rule 11.7 ("A cast shall not be performed between pointer to object and a non-integer arithmetic type") into rule 11.4, and rule 17.6 ("The declaration of an array parameter shall not contain the
statickeyword between the[ ]") into rule 17.5. The merged rules no longer exist as standalone checks and are removed from migrated profiles. If you had enabled only 11.7 or 17.6, enable 11.4 or 17.5 respectively to keep the corresponding coverage. - Directive 5.2 (deadlocks) resets to its default: MISRA C:2025 reports thread data races (Dir 5.1) and deadlocks (Dir 5.2) under two distinct directives, while the previous mapping in Teamscale covered both under Dir 5.1. The migration preserves your setting for Dir 5.1, whereas Dir 5.2 takes its default, which is off. If you rely on deadlock detection, enable Dir 5.2 manually.
- Checks removed by the Cppcheck update: The open-source check
iterators2("Same iterator is used with different containers (2)") was dropped in Cppcheck 2.21.0 and is removed from migrated profiles. It no longer produces findings and cannot be re-enabled, and there is no replacement.
2026.6 Removed Teamscale Jira Gadget
The Teamscale Jira Gadget, which allowed showing a Teamscale dashboard within a Jira dashboard, has been removed with version 2026.6.
2026.6 Deprecated Test Gap Overview widget
We are deprecating the Test Gap Overview widget. Its two main functions are now covered better by other widgets:
- List of partitions and their latest upload commit: View this information via the Included Coverage Uploads button on each Test Gap treemap widget, which opens a filterable dialog of all uploads considered in the treemap. If this is your only use case for the widget, you can simply delete it from your dashboards.
- Test Gap percentage as a big number: The Test Gap pie chart widget introduced in Teamscale 2026.5 shows the same number in an easier to read and visually more pleasing way. Replace the overview widget with a Test Gap pie chart widget.
Timeline:
- Starting with 2026.6, the widget shows a banner informing users about the deprecation.
- Six months after this release, the widget will no longer show its content, only its banner.
- Three months after that, the widget will be removed completely from all dashboards.
2026.4 Security: Teamscale now validates the OpenId Connect tokens using the identity provider's JSON Web Key Set (JWKS)
Action Required: Manual Configuration for OpenID Connect
To enable token signature validation, admins must manually provide the JWKS URL from their Identity Provider. Without this step, the new security validation will not be active.
Steps to Update:
- Go to Admin > Settings > Authentication
- Edit your OpenID Connect configuration
- Add your Identity Provider's JWKS URL and save
2026.4 Security: External Content dashboard widget sandboxed by default
The content rendered by the External Content dashboard widget now has sandbox="" set by default. This blocks scripts, popups, downloads, top-level navigation, form submission and same-origin access from within the embedded page. The change addresses a security risk where a malicious embedded site could redirect users (phishing), execute JavaScript (drive-by exploits) or trigger malicious downloads from within Teamscale.
As a consequence, embeds that rely on JavaScript (for example, dashboards from other tools) will no longer render. If you need such embeds, an administrator can opt back in by enabling Allow dynamic content in External Content Widget under Admin > Settings > Server Settings > Dashboards.
Security note: enabling this option allows embedded pages to execute arbitrary JavaScript and access their own origin. Only enable it if all URLs configured in External Content widgets across all dashboards are trusted.
2026.4 Renamed Java profiler Docker image to cqse/teamscale-java-profiler
Teamscale's Java profiler was previously published under the name cqse/teamscale-jacoco-agent. To ensure consistent and clear naming of our profilers, we renamed it to cqse/teamscale-java-profiler. This brings it in line with the naming for our .NET and JavaScript profilers. Thus, it is required to change the name of the Docker image you use to cqse/teamscale-java-profiler. The versioning scheme remains the same.
2026.4 Oldest supported IntelliJ raised to 2023.3
The oldest supported version for the IntelliJ plug-in was raised to version 2023.3.
2026.4 Default log4j2.yaml has changed
The default log4j2.yaml shipped under config/log4j2.yaml has changed in 2026.4. If you have customized this file in your installation, please review the new default and merge in your changes manually — otherwise the new defaults will be lost on upgrade.
You can download the new default configuration here:
2026.3 Removed PDB processing and related services
The ability to upload PDBs and raw .NET trace files for tracking line coverage has been removed with version 2026.3.
2026.2 Removed AllowAll Authenticator
For security reasons, the AllowAll Authenticator has been removed with version 2026.2.
2026.1 Java 25 Required (Teamscale server application)
Starting with version 2026.1, the Teamscale server will require Java 25 to be executed.
Action required: In case you are not using a Docker-based deployment, please make sure to update the JRE used for executing Teamscale to Java 25.
Re-Analysis when Upgrading
- When updating from 2026.8.x, drop-in.
- When updating from 2026.7.x or earlier, a full re-analysis via backup is required.
What's New for Teamscale 2026.8
Quality Control
Portfolio Overview
The new Portfolio view in the Dashboard perspective shows the quality of many projects on a single page, so you can see which ones need attention without going through them one by one. Each row is a portfolio entry. By default, every project has one entry that covers the whole project, and you can add entries for a branch or a path with their own threshold profile and quality goal. An entry query selects the entries of an overview, and you combine columns for metrics, test gaps, quality goals, manual assessments and tasks with treemaps and assessment distributions. Teamscale computes the values in the background, so the overview stays fast even for many projects.
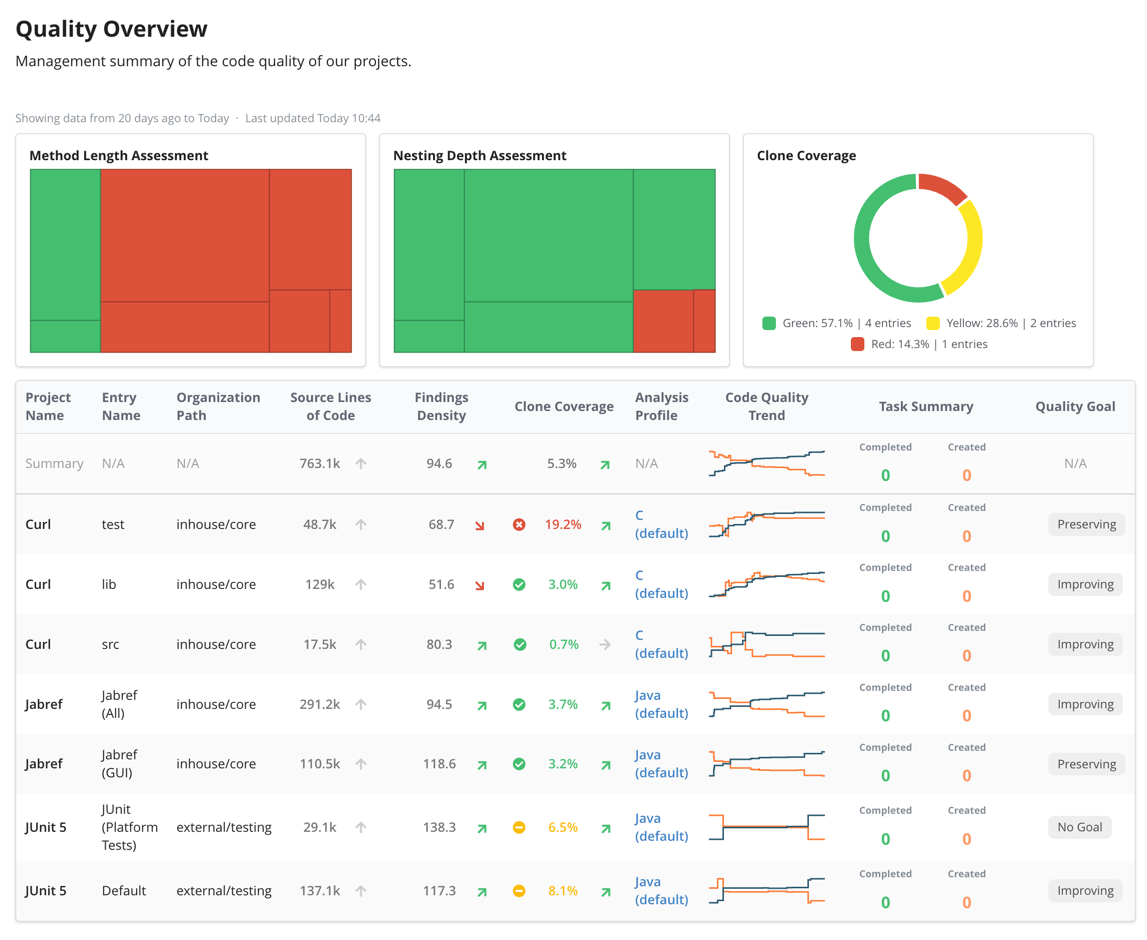
See the Portfolio view reference for details.
AI Features
Agentic Reviews
- The rating of review comments is simplified to Helpful or Not helpful / false positive. Existing Very helpful ratings are converted to Helpful.
- While a review runs, the Agentic Review tab of a merge request now shows the progress of each agent, including a log of its current activity.
- The new Link Review Agents project permission allows linking review agents to projects without the permission to edit the project.
Web Interface
Notification Center
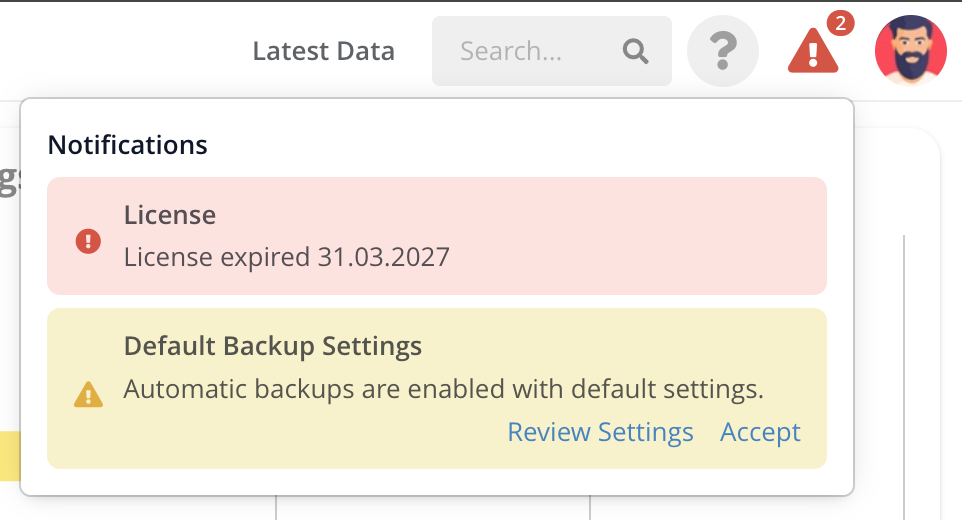
Instance-wide warnings and errors, for example about the license or the backup settings, are now collected in a popup in the top bar next to the user avatar, instead of being shown inline in the top bar.
Additional Improvements
- Dashboards now support showing metrics for multiple projects with different default branches, using the new Default branch of each project option.
- Dashboards can now be shared with the members of their projects directly when they are saved as a new dashboard, copied or created from a template.
- Accessibility: The architecture editor now supports the color-blind mode.
- Architecture Editor: When focusing a component, unrelated components are now dimmed instead of hidden, so you can still select them.
- The dialog for adding findings or code to an existing task now has an Add button per task, which shows a loading indicator while the task is updated.
Test Intelligence
- To make it easier to select a specific test budget, you can now drag the budget marker directly in the coverage over time chart of the Test Suggestions perspective.
JS Profiler
- The instrumenter now detects the commit automatically from the CI environment or the Git repository, so
--commitis optional. - The instrumenter now warns about files without source maps instead of reporting them as instrumented.
Change-Based Test Suggestions
- Added or changed tests are now always ranked first and marked with a NEW or CHANGED badge.
- The similarity scoring now always considers the title and description of linked issues.
Change-Independent Test Suggestions
- The Content-Based Suggestions tab now excludes tests with known testwise coverage by default, so it complements a suite assembled on the Coverage-Based Suggestions tab.
- The Coverage-Based Suggestions tab now counts only tests with testwise coverage, and explains why it is empty if none of the selected tests has any.
Software Composition Analysis
- Exclusion rules for uploaded vulnerability reports can now have a Maximum Severity, so a violation reappears when a later report rates it higher.
Analysis
- jQAssistant: Support for v2.10 including hidden findings.
- Simulink: In the block diagram view, opening a block whose library link is disabled now shows its local copy instead of the library block.
New Checks & Check Options
- Java: New "Dynamically formatted SQL query" check detects security-sensitive SQL query formatting (CWE-89) to help prevent SQL injection vulnerabilities.
- Objective-C/C++: 12 existing C/C++ checks are now also available for Objective-C and Objective-C++, covering switch statements, memory management functions and empty blocks, among others.
- JavaScript/TypeScript: Added 16 checks for React Hooks and one check for React Fast Refresh from the ESLint plugins
eslint-plugin-react-hooksandeslint-plugin-react-refresh. - C/C++: The comment completeness analysis now recognizes Doxygen member groups, so one comment documents all members of a group.
- Updated the integrated Dart Lint to version 3.13.4, including 28 new checks.
Guideline Support
- Teamscale now includes the 2025 version of the OWASP Top 10, so you can select it in findings filters, the check explorer, and guideline summary widgets. The mapping also covers PHP and ABAP checks.
Plugins & Integrations
- Eclipse Plugin: The new Teamscale > Verify IDE Configuration context menu entry checks whether the
.teamscale.tomlfiles of a project are set up correctly.
Command-Line Clients
- The
teamscale-dev pre-commitcommand has a new--cleanoption that empties the pre-commit branch before the upload. teamscale-uploadnow supports uploading vulnerability reports to Teamscale.
ABAP
- The retrieval of ATC check descriptions can now be switched off or pointed to a custom URL, including protocol and port, per SAP system connection.
- SAP systems that Teamscale cannot reach via RFC can now push their ABAP exports to a new API endpoint over HTTPS.
Administration & Operation
- Teamscale can now derive the OpenID Connect redirect URI from the request, so the same configuration works across environments with different base URLs.
- The Prometheus endpoint now exposes the usage of the Cppcheck, clang-tidy, and PSScriptAnalyzer process pools, so you can see whether these integrated tools slow down the analysis.
- The Load Backup From Other Instance tab now lets you pick which projects to include, instead of always pulling every project visible on the remote instance.
- Instance Comparison: The project configuration comparison now shows the changes of each code scope in a separate table.
- External storage (S3): Uploads can now be deleted from the External Report Uploads view, which also deletes their files in external storage.